Vendor Assurance for AI and Cloud-Based GxP Systems: What You Can Leverage, Challenge, and Independently Verify
A risk-based framework for vendor assurance of AI-enabled and cloud-based GxP systems: which vendor evidence you can leverage, which claims you must challenge, and which controls or outcomes you must independently verify.

EO Sterilization Validation and Revalidation Under ISO 11135: Practical Implementation and Lifecycle Considerations
Learn the ISO 11135 requirements for EO sterilization validation and periodic revalidation — covering equipment IQ/OQ/PQ, overkill approach, sterile load V&V, BIs/PCDs, and lifecycle controls for medical devices.
 John E. Lincoln

Beyond Digital Batch Records: Managing FDA and EU GMP Documentation While Preserving Data Integrity
Learn how digital/electronic DHF, DMR, DHR, and EU MDR Technical Documentation improves data integrity, reduces human error, and simplifies global regulatory compliance.
John E. Lincoln
Configuration Control vs. Document Control – Managing Design Changes Across Modern Quality Systems
Learn why Configuration Architecture — not Document Control — defines the modern Quality System, and how treating relationships as first-class objects strengthens traceability, change control, and inspection readiness.
 José Mora
QMSR Device Records: Structuring DDF, MDF and Related Relationships for Inspection Readiness
Learn how to structure QMSR Device Records using Lean Documents and Lean Configuration principles to achieve true inspection readiness through relationship integrity, not just document control.
José Mora
ChatGPT-Assisted Technical Writing
Learn practical, compliant approaches to using ChatGPT for SOP drafting, document development, and technical writing in regulated industries.
 Charles H. Paul
Using SPC and Process Data to Support Quality, Stability, and Manufacturing Decisions
Learn how SPC, Six Sigma, and process data support CGMP production controls — sampling plan justification, verification/validation, and trend analysis for non-conformances, complaints, and CAPAs.
John E. Lincoln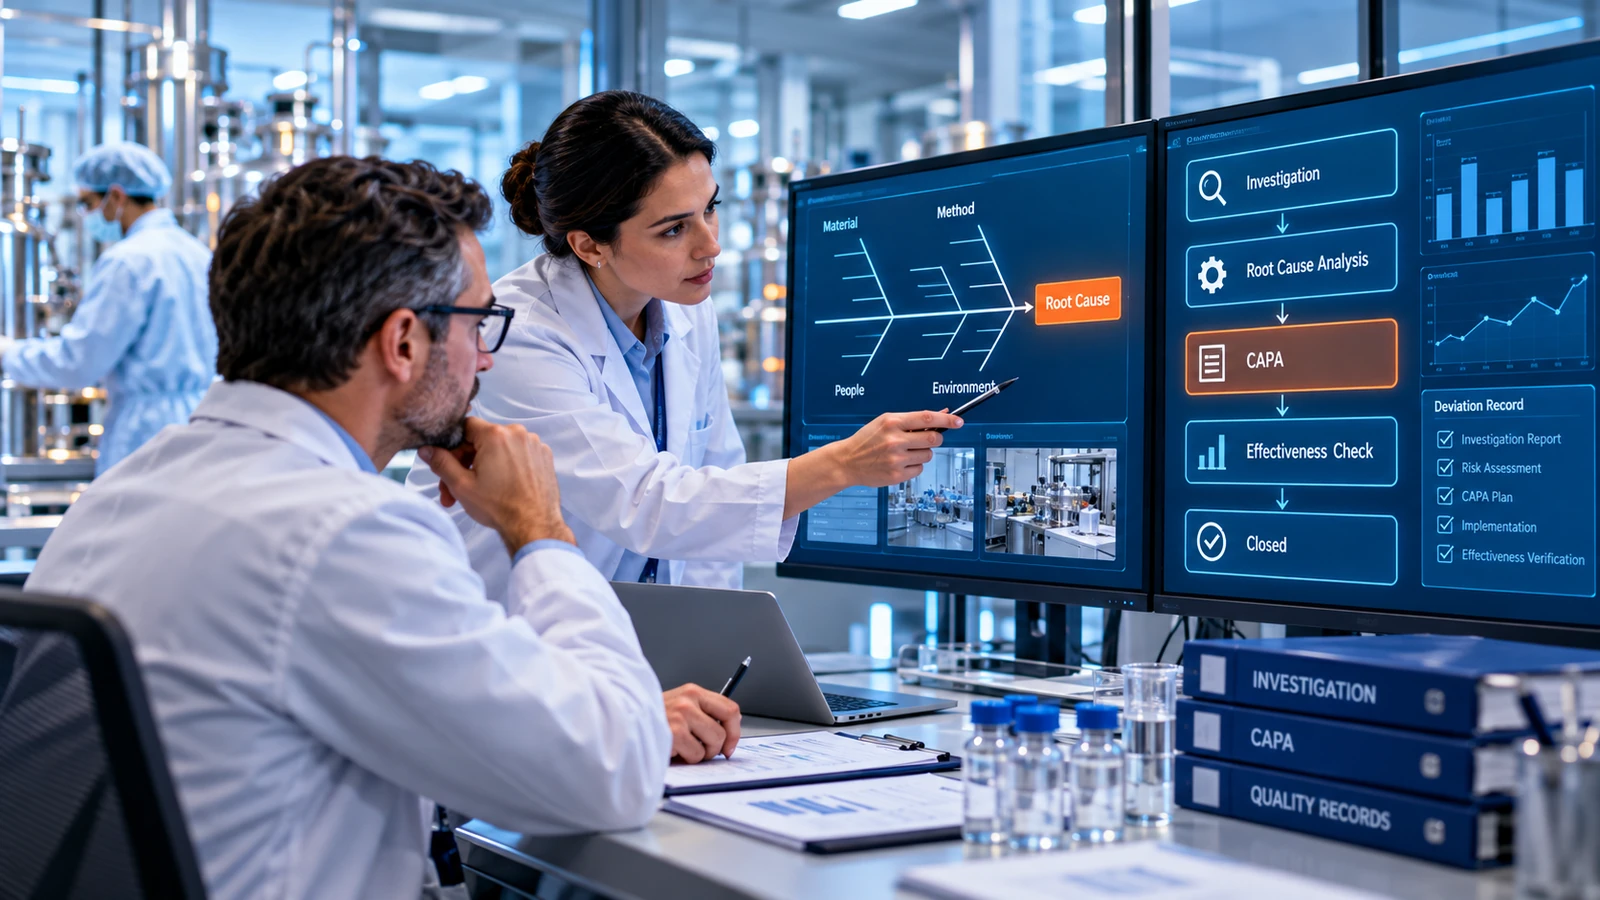
Root Cause Analysis for GMP Investigations: Identifying Systemic Failures and Building Effective CAPA
Master closed-loop CAPA with repeatable failure investigation and root cause analysis tools that satisfy FDA audit expectations in GMP environments.
John E. Lincoln
Data Integrity: What Exactly Is Required for 21 CFR Part 11, SaaS/Cloud, EU GDPR
Get complete clarity on 21 CFR Part 11, Annex 11, SaaS/Cloud compliance, AI software validation, and EU GDPR requirements for regulated industries.
 David Nettleton

Risk-Based CSV/CSA for Modern GxP Systems: Making Defensible Validation Decisions in Practice
A two-day, risk-based framework for CSV/CSA and GAMP® 5 validation decisions on modern GxP systems — cloud, SaaS, configurable, and AI-enabled platforms — built for inspection readiness.
 Carolyn Troiano
Acceptance Criteria for AI Validation: Determining What "Reliable" Actually Means in GxP Systems
Learn how to define meaningful, risk-based acceptance criteria for AI systems in GxP environments — covering reliability thresholds, hallucination controls, human guardrails, and CSA-aligned validation strategies.
Carolyn Troiano
Audit Trail Review by Exception: Reducing Reviewer Burden Without Weakening Detection
Learn how to implement a risk-based audit trail review-by-exception strategy that reduces reviewer fatigue while strengthening detection of critical compliance, data integrity, and cybersecurity risks.
Carolyn Troiano